


Pentest en entreprise, audit de code et phishing simulé : trouver vos failles avant les attaquants
Un pentest en entreprise simule une vraie cyberattaque contre votre système d'information pour trouver les failles exploitables avant un attaquant. IT Systèmes le réalise pour les PME et les ETI, en externe comme en interne, et le complète par un audit de code et des campagnes de phishing et de vishing simulées : vos défenses techniques et vos équipes sont mises à l'épreuve dans des conditions contrôlées, puis vous recevez un plan de correction classé par priorité.
By combining regular audits, code reviews, simulated phishing and vishing campaigns, and tailored training, companies can significantly reduce their risks and become more mature in dealing with threats. The first step in any security initiative isan IT security audit, which identifies precisely which vulnerabilities need to be addressed as a priority.
Penetration testing, security audits, intrusion testing: What are we talking about?
A penetration test (or penetration test) involves simulating a real cyberattack against your information system, conducted by experts, to identify exploitable vulnerabilities before an attacker does. It is a practical test of your defenses, whereas a security audit provides a broader analysis of your configurations, processes, and organization.
Depending on the level of information provided to testers, there are three approaches:
- Black box: no prior access or information, just like an external attacker.
- Grey box: limited access (a standard user account), to simulate a malicious employee or a compromised account.
- White Box: Full access to the code and architecture, for the most comprehensive analysis.
Tests can be external (from the Internet) or internal (from your network). In addition, there are simulated phishing and vishing campaigns, which test the human factor—often the root cause of successful attacks. IT Systèmes combines these approaches based on your actual exposure.
Our audit, pentest and awareness expertise
Technical and organizational cybersecurity assessment
External and internal pentesting
Simulated phishing and vishing campaigns
Audit Active Directory and Entra ID
Cyber awareness and training programs
Source code audit and development review
Why work with IT Systèmes?
- Quickly identify security vulnerabilities before they are exploited.
- Check the robustness of your defenses with realistic tests.
- Guarantee application security with specialized code audits.
- Réduire les risques liés à l'erreur humaine, à l'origine de nombreuses cyberattaques réussies, avec des campagnes de phishing et de vishing simulées et des formations ciblées.
- Improve compliance with regulations (RGPD, ISO 27001, NIS2).
- Develop a genuine cybersecurity culture within your teams.
Learn more:
→ Surveiller vos systèmes avec notre SOC managé.
→ Learn more about our cybersecurity and compliance expertise.
Penetration Testing for Small and Medium-Sized Businesses: How Often, and at What Cost?
A penetration test tailored to your size
SMEs and mid-sized companies are now prime targets, as they are often less secure than large corporations. A penetration test is no longer reserved for large organizations: we tailor the scope, depth, and budget to your actual risk exposure, without overdoing it.
- Targeted scope: We focus on the most critical assets (Internet exposure, business applications, Active Directory / Entra ID) rather than conducting a blanket audit.
- How often? An annual test, to be conducted after any major change (new application, migration, launch of a service). Regular penetration tests are increasingly required by cyber insurance providers and standards (ISO 27001, NIS2).
- Un livrable actionnable : rapport clair, failles classées par criticité et plan de remédiation priorisé, pas une liste brute de vulnérabilités.
- Support for remediation: We don’t stop at identifying issues—we help your teams close the gaps.
Need some guidance? We'll provide a quote within 48 hours.
Campagne de phishing simulée : comment ça se passe
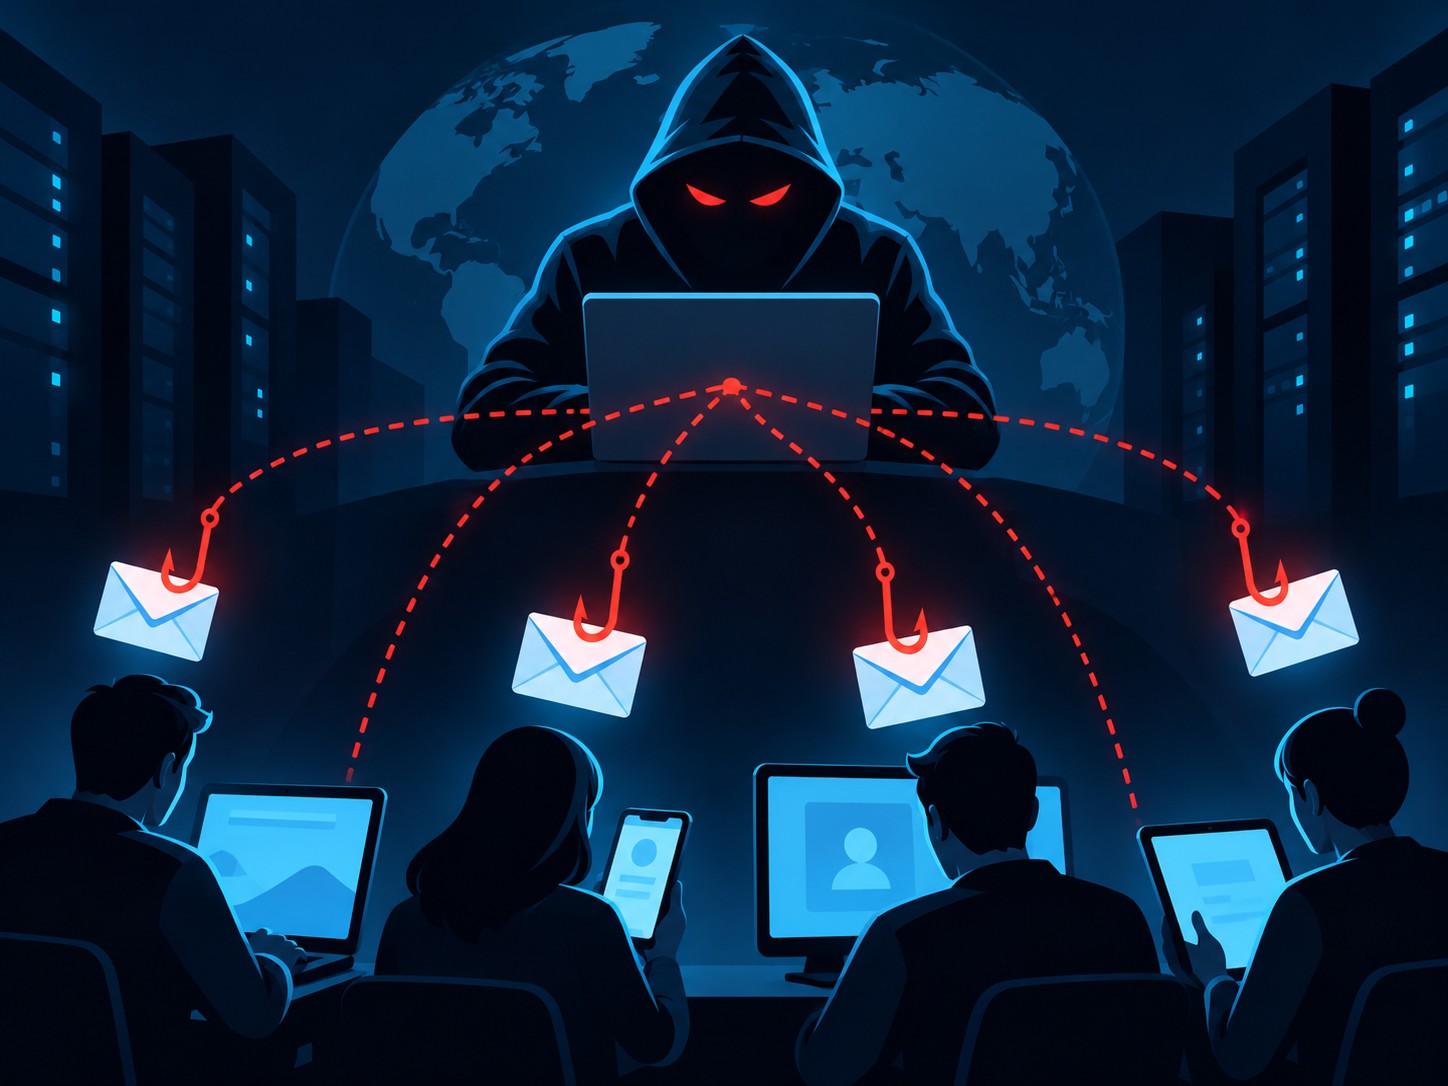
Une campagne de phishing simulée envoie à vos collaborateurs de faux e-mails piégés, préparés par nos experts, pour mesurer leurs réflexes sans mettre l'entreprise en danger. Elle se déroule en cinq temps.
- Cadrage avec la direction : objectifs, collaborateurs concernés, scénarios autorisés et calendrier, validés avec vous avant tout envoi.
- Préparation des scénarios : faux e-mails inspirés des attaques réelles (fausse facture, faux partage de document, faux message du service informatique) et, si vous le souhaitez, appels de vishing.
- Envoi sur la période convenue, dans des conditions contrôlées.
- Mesure des réactions : qui a ouvert le message, cliqué, saisi des informations, ou au contraire signalé la tentative.
- Restitution et formation : résultats présentés à la direction, retours individualisés et formations ciblées pour les profils les plus exposés, puis une nouvelle campagne pour mesurer les progrès.
Initial diagnosis and scoping
Tests and evaluations
Analysis and prioritization of results
Feedback and recommendations
Training and long-term support







Questions fréquentes sur le pentest en entreprise, l'audit et la sensibilisation
What's the difference between a security audit and a pentest?
A security audit involves an in-depth analysis of systems, configurations and processes to identify potential vulnerabilities. It's a methodical, exhaustive approach, often based on reference frameworks (ISO 27001, CIS, ANSSI), while a pentest, or penetration test, simulates a real attack to assess the ability of defenses to detect and counter an intrusion. The two approaches are complementary: an audit provides an overall view of weak points, while a pentest verifies the actual robustness of systems.
Why perform an Active Directory or Entra ID audit?
Active Directory et Entra ID (anciennement Azure AD) sont des composants stratégiques car ils gèrent les identités et les accès. Une mauvaise configuration ou des droits excessifs peuvent donner aux attaquants une porte d’entrée directe vers tout le système d’information.Un audit AD/Entra ID permet de détecter les comptes dormants, les mots de passe faibles, les failles de configuration et les accès à privilèges mal sécurisés. Ce type d'audit est devenu incontournable : l'annuaire est l'une des premières cibles d'un attaquant, car il ouvre l'accès à tout le reste du système d'information.
What is the purpose of a source code audit in cybersecurity?
A source code audit, or security code review, enables you to detect logical and technical vulnerabilities directly in the software you develop or use. This analysis can be carried out using static analysis tools (SAST), which examine the code without executing it, and dynamic tools (DAST), which test the application's behavior in operation. Code auditing is particularly critical for web, mobile and business applications: by securing the code at source, we reduce the cost of correction, improve software quality and limit the risks of exploitation once the application is in production.
Why are simulated phishing campaigns useful?
Simulated campaigns reproduce the techniques used by cybercriminals, by sending fake emails to employees. The aim is to measure their vigilance, identify vulnerable users and offer targeted training. This approach helps to gradually improve the maturity of teams, while creating a culture of vigilance. It's an effective method, because it confronts users with real-life situations, without endangering the company.
Why raise employee awareness when there are technical safeguards in place?
Même les meilleurs outils de sécurité ne suffisent pas si les utilisateurs commettent des erreurs (clic sur un lien frauduleux, partage de données sensibles, usage de mots de passe faibles). Une grande partie des cyberattaques réussies commence par une erreur humaine.La sensibilisation complète les protections techniques. Elle transforme les collaborateurs en première ligne de défense, capables d’identifier et de signaler des comportements suspects. Une entreprise qui investit dans la formation réduit considérablement son exposition aux risques.
Are audits, pentests and code audits mandatory for compliance?
Most standards require regular security checks: ISO 27001 imposes tests and verifications, the RGPD demands proof of personal data protection, and NIS2 insists on proactive vulnerability management. Although not always explicitly mentioned, audits, pentests and code audits are essential means of demonstrating compliance and proving that protection measures are not just theoretical.
In addition to regulatory requirements, cyber insurers are increasingly demanding proof of regular audits before issuing or renewing coverage. Without such proof, companies may be denied compensation in the event of a claim. Similarly, some customers and partners impose audits and pentests as a prerequisite for signing or maintaining a contract, particularly in sensitive sectors such as finance, industry or healthcare.
In practice, even when they are not explicitly required by law, audits, pentests and code audits are becoming indispensable for obtaining appropriate assurances, gaining customer confidence and maintaining a credible, verifiable security posture.
Why include vishing in awareness campaigns?
Vishing (social engineering by telephone) exploits trust and urgency to obtain sensitive information or induce an employee to perform a dangerous action. Unlike phishing by email, vishing can bypass certain technical protections and reach people with less training in the risks involved.Simulating vishing enables us to assess the real vulnerability of teams to scenarios involving impersonal calls, identity theft or psychological manipulation. By combining phishing, spear phishing and vishing, you can cover the full range of social engineering vectors and strengthen your organization's human resilience.
What is the methodology for an IT security audit?
An IT security audit follows seven steps: defining the scope, mapping assets, scanning for vulnerabilities, intrusion testing, auditing policies and access, analyzing risks, and reporting on the action plan. See our comprehensive guide: IT security audit: method, steps, and SME checklist.